Products
TRAIODerScannerSonatypeHashiCorp VaultDPA FASTBurp DASTBurp ProfessionalDevSecOps services by TRIDS
Services
DevSecOps implementationApplication security assessmentAppSec & DevSecOps training
Company
About usCareers & internshipsAppSecFestSonatype User GroupPrivacy policyBlogContacts
Language
RUKZENUZ
+7 777 734 7070 Get a consultation
Burp Suite DAST

Burp Suite DAST in Kazakhstan: automated DAST scanning

Scale your AppSec, unburden your security team. Automated DAST scanning without limits. Built on the Burp technology your security teams already trust.
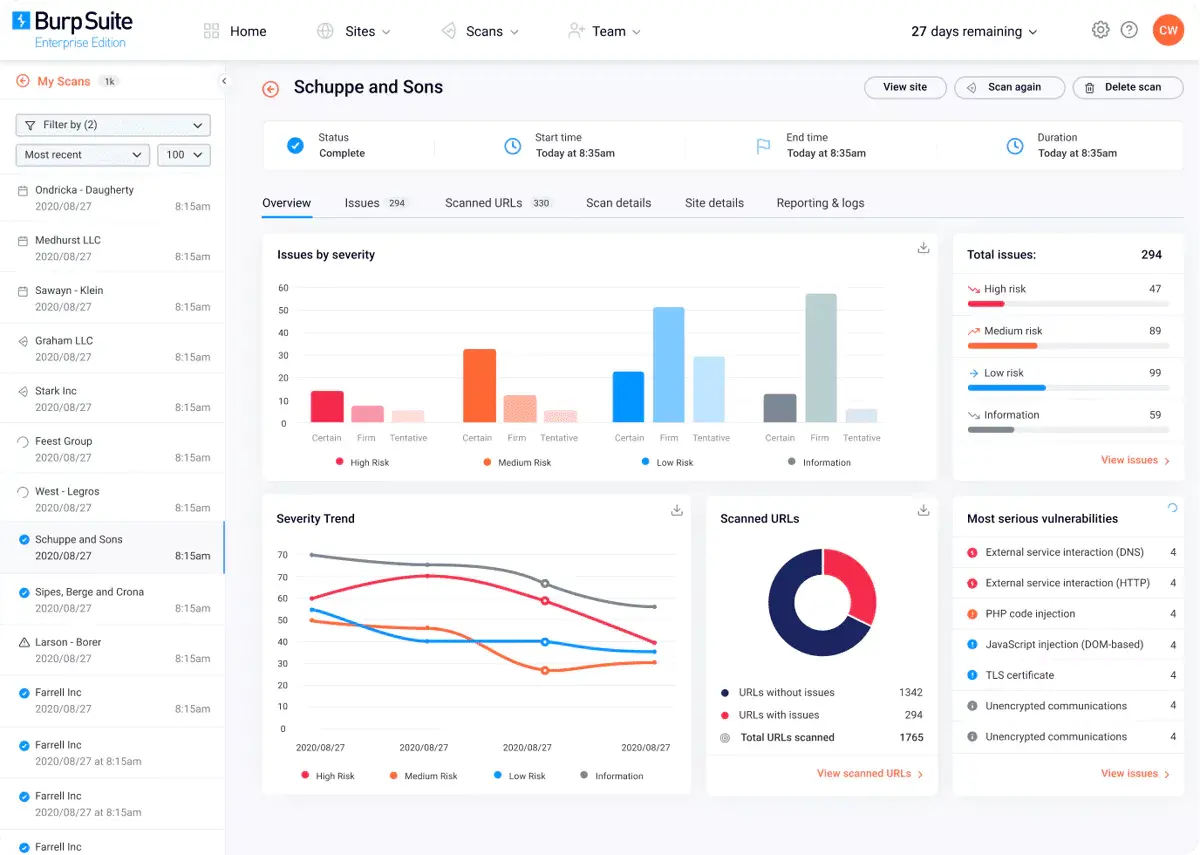
Burp Suite DAST · Dashboard
Burp Suite DAST dashboard
Secure your whole web portfolio

Scale without resource limitations. Automate trusted dynamic scans right across your portfolio.

Integrate security with development

Remove bottlenecks. Integrate dynamic scanning, see fewer false positives, and avoid alert fatigue.

Free time for AppSec to do more

Contribute without constraining development. DevSecOps frees AppSec time to do more.

What's new

Discover DAST without disruption

Smarter authentication, stronger API scanning, and improved scan orchestration. Learn about the latest evolution of Burp Suite DAST.
Burp Suite DAST
Secure your whole web portfolio
Set up with ease, report with simplicity
Perform recurring dynamic (DAST) scans across thousands of sites. Use bulk actions to manage scanning at scale, or set sites up individually; all you need is a URL.
Make your security posture visible
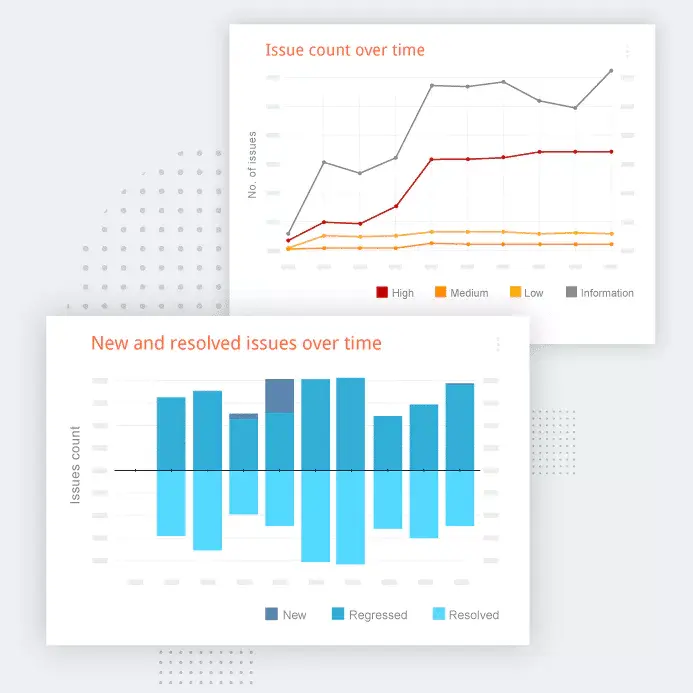
Intuitive dashboards help to identify trends over time. Get scan reports by email, export to other tools, and produce reports for individual compliance standards.
DevSecOps integration
Easy integration with any CI/CD platform, native support for Jira, GitLab, and Trello, and a rich GraphQL API — to easily incorporate security within your existing software development processes.
Reduce risk without increasing costs
Subscription options that enable companies of any size to scan at scale. Maximum ROI — with no strings attached.
Issues over time
Integrate security with development
Bake security into software development processes
A wide range of integrations (e.g. CI/CD, issue tracking platforms, and a rich GraphQL API) mean you can bake security into your software development.
Security technology, accessible for all
Get fast, easily-digested feedback on vulnerabilities, tailored to you. Use role-based access control (RBAC) and single sign-on (SSO) to manage teams.
Join forces to fix vulnerabilities
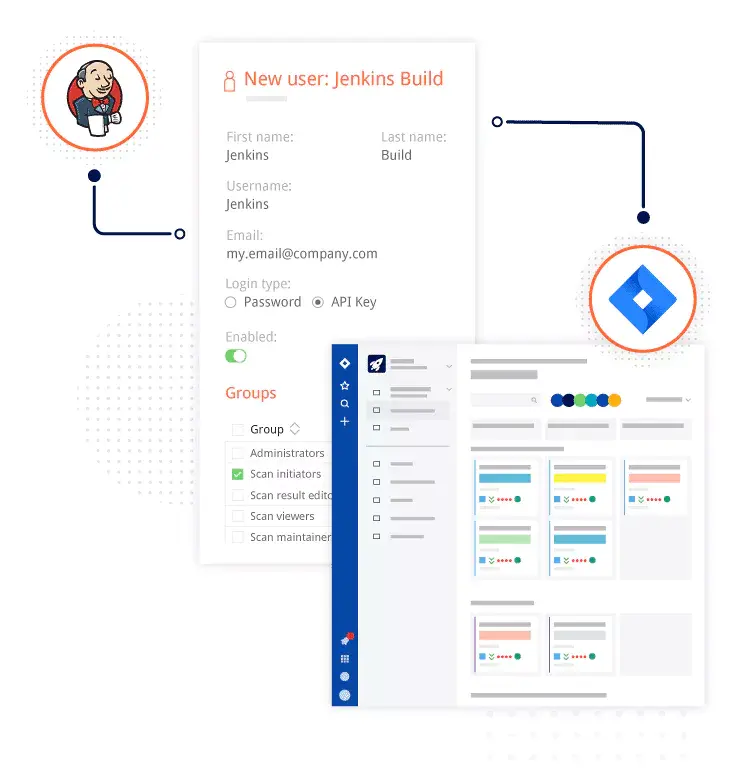
Integrate with Jira, GitLab, or Trello, and enable developers to collaborate with AppSec teams to remediate critical issues.
Jenkins and Jira integration
Free time for AppSec to do more
Free time to eliminate vulnerabilities
Always-on scanning keeps your reports up to date. Prioritize vulnerabilities using filters to deal with them effectively.
Work with Burp Scanner
Gold standard scanning, powered by PortSwigger Research and trusted at over 17,000 organizations worldwide. With remediation for every vulnerability you find, it's designed to scan the modern web.
Customize and control
Take control with custom scan configurations and Burp extensions (BApps) — to help you hunt down even the trickiest bugs while minimizing false positives.
Burp Scanner
17 000+ organizations

Powered by Burp Suite technology trusted at over 17,000 organizations worldwide

The same Burp Scanner you know and love — scaled for the enterprise. Driven by PortSwigger's world-leading cybersecurity research team, it can find everything from classic bugs to the very latest vulnerabilities.

Burp Scanner's dynamic (DAST) approach maximizes coverage, while minimizing false positives, without the need to instrument code. In fact, it's capable of finding many critical vulnerabilities that even an experienced manual tester could miss.
Brands around the world using Burp Suite
Burp Suite DAST frees our AppSec team to spend their time where it's most valuable.
Cal Poly
Customer case studyCalifornia Polytechnic State University · portswigger.net

Scale your Application Security with the Best of Breed DAST Scanner

Request demo
Burp Suite DAST in Kazakhstan

Burp Suite DAST for companies in Kazakhstan and Central Asia

Burp Suite DAST (formerly Burp Suite Enterprise Edition) scales the proven Burp Scanner technology across your entire portfolio of web applications and APIs. We will help you purchase licenses and embed scanning into CI/CD.

  • Selecting the edition and calculating Burp Suite DAST license costs for your needs
  • Demo and assistance with running a pilot on your infrastructure
  • License supply and closing documents for legal entities
  • Deployment and integration into CI/CD, repositories and issue trackers
  • Technical support and maintenance in Russian
  • Training for development and AppSec teams
Kazakhstan and Central Asia

Office in Almaty. We work with companies across Kazakhstan and in Central Asian countries: Uzbekistan, Kyrgyzstan, Tajikistan and Turkmenistan.

AlmatyAstanaShymkentAtyrauKaragandaTashkentBishkekDushanbeAshgabat
FAQ

Frequently asked questions about Burp Suite DAST

How does Burp Suite DAST differ from Burp Suite Professional?
Professional is a pentester's tool for manual and semi-automated testing. DAST (Enterprise) is a platform for regular automated scanning of thousands of sites, with dashboards, RBAC, SSO and CI/CD integrations.
Does Burp Suite DAST integrate with CI/CD and Jira?
Yes: it has integrations with any CI/CD platform, native support for Jira, GitLab and Trello, and a GraphQL API.
How do I buy Burp Suite DAST in Kazakhstan?
Leave a request. We will select a subscription based on the number of applications, prepare a quote and closing documents, and help with deployment.
Consultation

We protect your applications at every stage of development.

Tell us about your challenge — AST Cyber Lab experts will select a solution, run a demo and help with implementation.