DPA FAST in Kazakhstan: security testing of frontend applications
FAST analyzer for automated security testing of frontend applications within secure software development (SSDLC / DevSecOps).
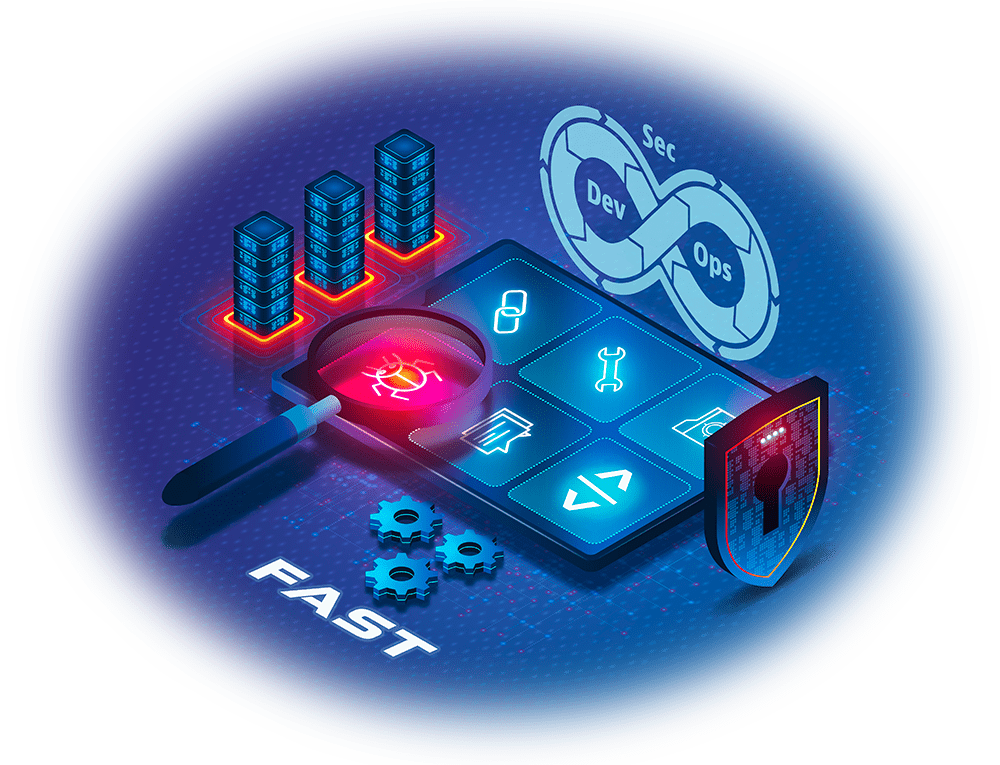
Classic analyzers do not see all threats
Classic analyzers (SAST, DAST, SCA, OSA) used in secure development do not detect all threats specific to client-side JavaScript/TypeScript applications, such as loading third-party code and executing encrypted code from text. Reliably identifying all code that is actually executed and the malicious behavior of scripts is only possible at the browser's Content Layer.
Frontend applications have dozens of dependencies, and during development they are not analyzed for real threats. This creates a security blind spot and gives attackers a way to monetize a breach, as regularly seen in real attacks. All of this code has full access to the web application page and browser functions and can perform the following actions.
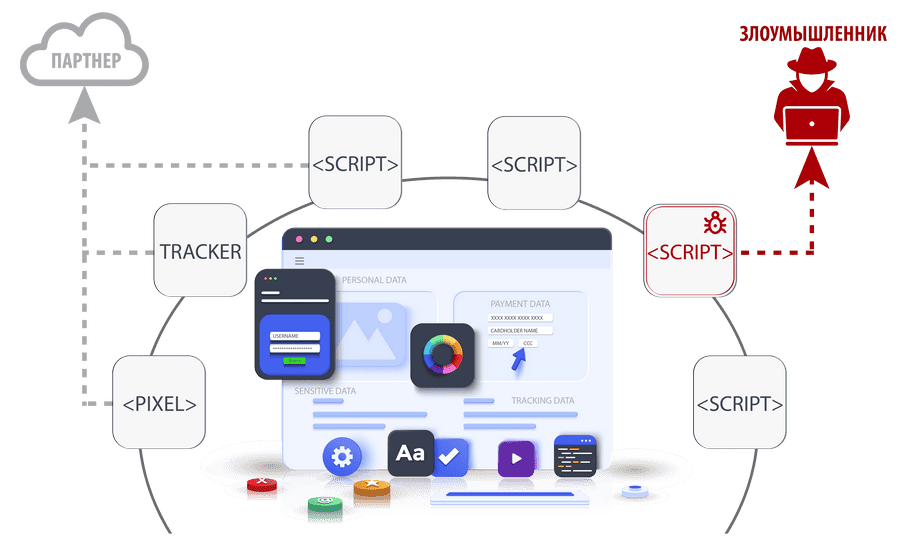
Collecting and stealing critical data from web application pages (personal data, bank cards, customer data, accounts, tokens, cookies, behavioral profiles, etc.)
Loading other attacker scripts onto the page
Performing actions on behalf of the user
Showing the user fraudulent banners on behalf of the company to later steal money or data, or to deliver a malicious attachment
Cryptocurrency mining using the user's device computing resources
Infecting the user's device by exploiting browser vulnerabilities
Security of frontend applications
- Undeclared capabilities and backdoors in js library dependencies
- Excessive data transfer to trusted partners
- Unauthorized modification of files on compromised CDNs
- Supply chain attacks on frontend applications
- Data leaks through the browser from intranet portals (CRM, HRM, ERP, Wiki)
- Improper access control and business logic vulnerabilities (incl. IDOR)
- Display of fraudulent banners on behalf of the company
- Excessive data exposure by the developer (OWASP API3:2019)
- Disclosure of critical data in comments within web page and script code
- Black-hat SEO (link selling, competitors' retargeting scripts)
- Trackers / tracking pixels
- Tag management systems
- Cross-border transfer of personal data
- Malicious browser plugins
DPA FAST Analyzer
DPA FAST Analyzer is a Russian FAST analyzer for automated security testing of frontend applications within secure software development (SSDLC / DevSecOps).
The tool analyzes script behavior, detects undeclared capabilities and backdoors in third-party libraries, lets you enforce information security policy requirements for client-side js/ts application development, and manages the attack surface to release frontend applications under the Secure by Design principle.
Three levels of control
Using frontend-sandbox technology, FAST analysis executes all js code, including dynamically loaded code. Besides scripts, other active elements are detected (event attributes, iframe, object, and others).
The output is a complete, reliable Frontend SBOM and a list of deviations from the reference security policy that require a response from an AppSec specialist.
To achieve its goal, an attacker's script will need to make a network request from the frontend application page (for example, to download a payload or send stolen data).
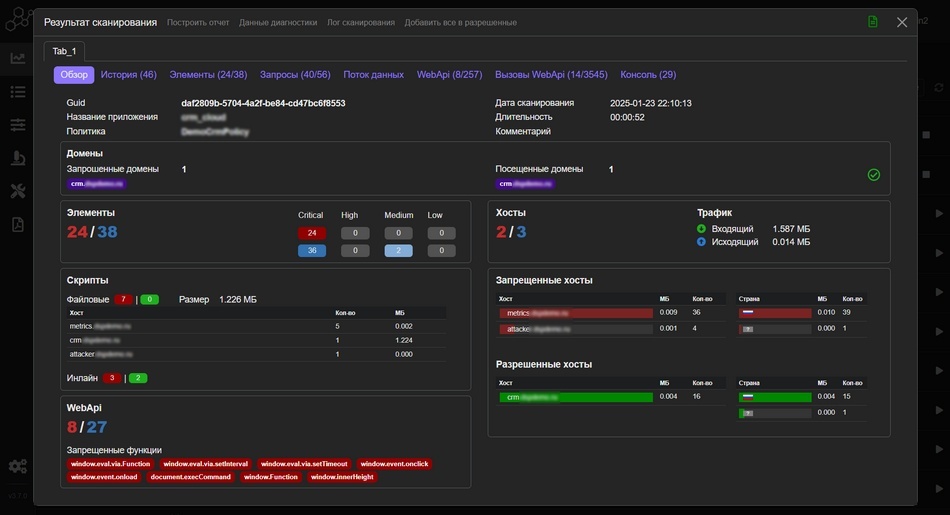
The FAST analyzer monitors all network requests at the browser content layer and displays a Data Flow Diagram. If a request to an unauthorized host is detected, a security policy violation is recorded.
You can also analyze what data (composition / volume / destination country) partner services collect.
Modern browsers give js applications many APIs that attackers can abuse (access to the camera, microphone, screen, notifications, geolocation, fullscreen mode, clipboard, saved payment methods, and others). At the same time, most frontend applications use no more than 2% of the available APIs.
When analyzing script behavior, the FAST analyzer detects calls to such APIs. If, after updating third-party libraries, an application starts requesting microphone access, this may indicate a backdoor inserted into the code by an attacker.
Using the FAST analyzer, you can monitor calls to browser APIs that are not allowed.
Integration into the development process
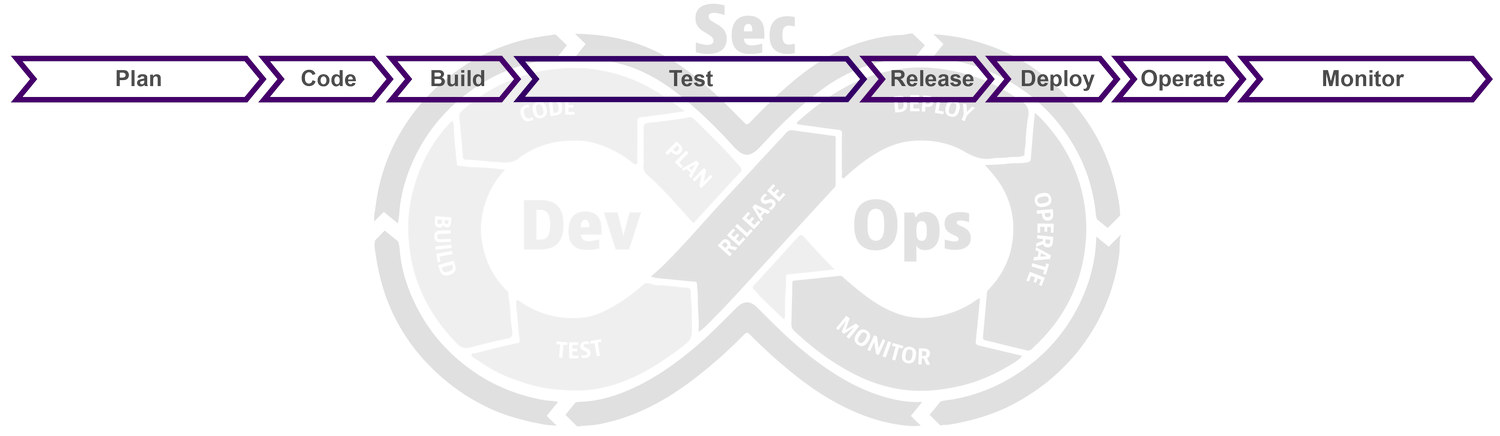
- Define a policy for active elements (for example, iframes are prohibited)
- Define a policy for data-receiving hosts
- Define a policy for allowed dangerous browser functions (for example, only geolocation access is permitted)
- 1. Run a FAST analyzer scan
- 2. Complies with policy: release allowed
- 3. Does not comply with policy: AppSec specialist approves the deviation; policy is adjusted or the violation is fixed; rescan
- 1. Periodic FAST analyzer scanning of the production version
- 2. Does not comply with policy: incident investigation
Problems we solve
- A manageable and measurable risk-based process for developing secure frontend applications
- Attack surface control in a js application, detection of "dangerous" browser APIs in use
- Detection of current threats and vulnerabilities in frontend applications that are invisible to classic security analyzers (SAST, DAST, SCA, OSA)
- Ability to analyze data collected by trusted partners for redundancy and cross-border transfer
- Prevention of information leaks in frontend applications, including web skimming (e-skimming) and formjacking attacks
- Automated security analysis without increasing Time to Market (TTM)
- Detection of backdoors, compromise indicators and undeclared capabilities in dependencies based on anomalous application behavior
- Compliance with PCI DSS 4.0, Russian Federal Law 152-FZ, NKCKI, GDPR and industry information security standards. Reports for auditors
- Inventory of all scripts and other active elements, integrity control
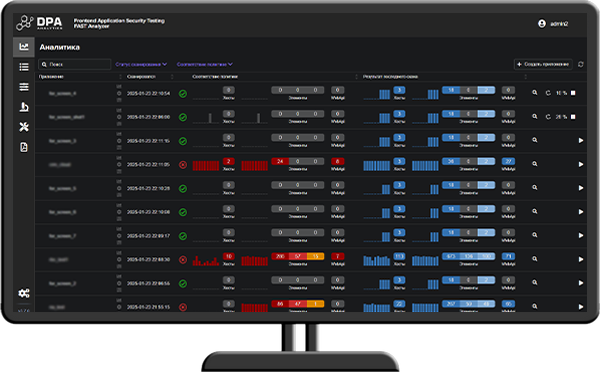
What DPA FAST looks like
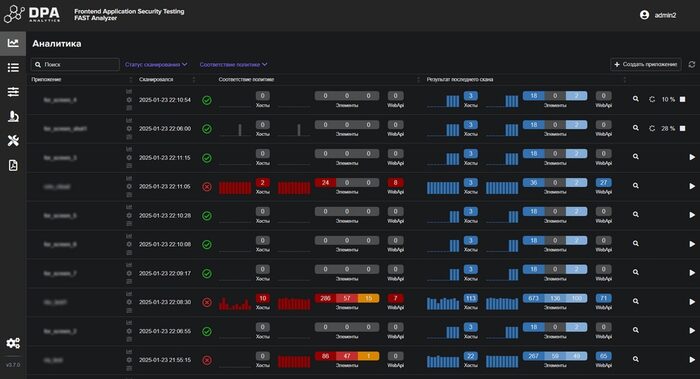
Why FAST analysis
Frontend Application Security Testing (FAST) analyzer detects current threats to client-side JavaScript applications that other security analyzers cannot see.
Control the security of every release within secure development to prevent data leaks and attacks on users.
The FAST analyzer applies policies on an "allowlist" principle. After initial policy setup, an alert is raised only when an element or action representing a real violation that requires an AppSec specialist's response is detected.
To set up the first scan, you need a test environment with the frontend application. Configuring a basic E2E scenario takes a few minutes in a convenient UI.
Scanning runs against specific E2E scenarios and does not exceed their duration, so it does not affect Time to Market (TTM).
The FAST analyzer works with frontend-sandbox technology, executing all js code in a modernized virtual browser. It monitors dynamic code injection, network requests and browser API usage.
Secure development of frontend applications and releasing every build on the Secure by Design principle
Deploying DPA FAST in Kazakhstan and Central Asia
We help banks, fintech, e-commerce and telecom companies control the security of client-side JavaScript code: from third-party scripts and CDNs to cross-border transfer of personal data.
- Selecting the edition and calculating DPA FAST license costs for your needs
- Demo and assistance with running a pilot on your infrastructure
- License supply and closing documents for legal entities
- Deployment and integration into CI/CD, repositories and issue trackers
- Technical support and maintenance in Russian
- Training for development and AppSec teams
Office in Almaty. We work with companies across Kazakhstan and in Central Asian countries: Uzbekistan, Kyrgyzstan, Tajikistan and Turkmenistan.