TRAIO, an application security management platform inside your own perimeter
SAST, SCA, DAST, secrets and containers in one platform. Built for Kazakhstan's banks and government sector, meeting ARDFM Resolution No. 53 and the Unified Requirements (UR). On-Premise only.
Solutions by task and industry
SAST and library analysis that regulators require, out of the box and inside your own perimeter.
Deploys on your infrastructure and requires no outbound connections.
1C code is checked on the same platform and lands in the same vulnerability list as the rest of your stack.
Check results for every version are collected continuously, not two weeks before an audit.
Full Application Security stack
Specialized tools for every level of security, in one interface.
Source code analysis for vulnerabilities across 30+ languages: C#, C, C++, Go, Kotlin, Java, JavaScript, PHP, Python, Ruby, Rust, Scala, Swift, TypeScript. Engines include Semgrep, Bandit, ESLint and others.
Testing of a running application: scanning of web applications and APIs, checks of authentication and authorization, the things SAST cannot see.
CVEs in third-party libraries for Maven, NuGet, npm, pip, bundler and others. SBOM in CycloneDX and SPDX formats. OWASP Dependency-Check, Dependency-Track, Trivy, Syft.
Search for API keys, passwords and tokens in code and git history (TruffleHog, Gitleaks), preventing credential leaks.
Scanning of Docker images and Terraform, Kubernetes, Helm and Dockerfile configurations for vulnerabilities and misconfigurations (Trivy, Checkov).
Static analysis of APK and IPA files: Android and iOS platforms, binary analysis.
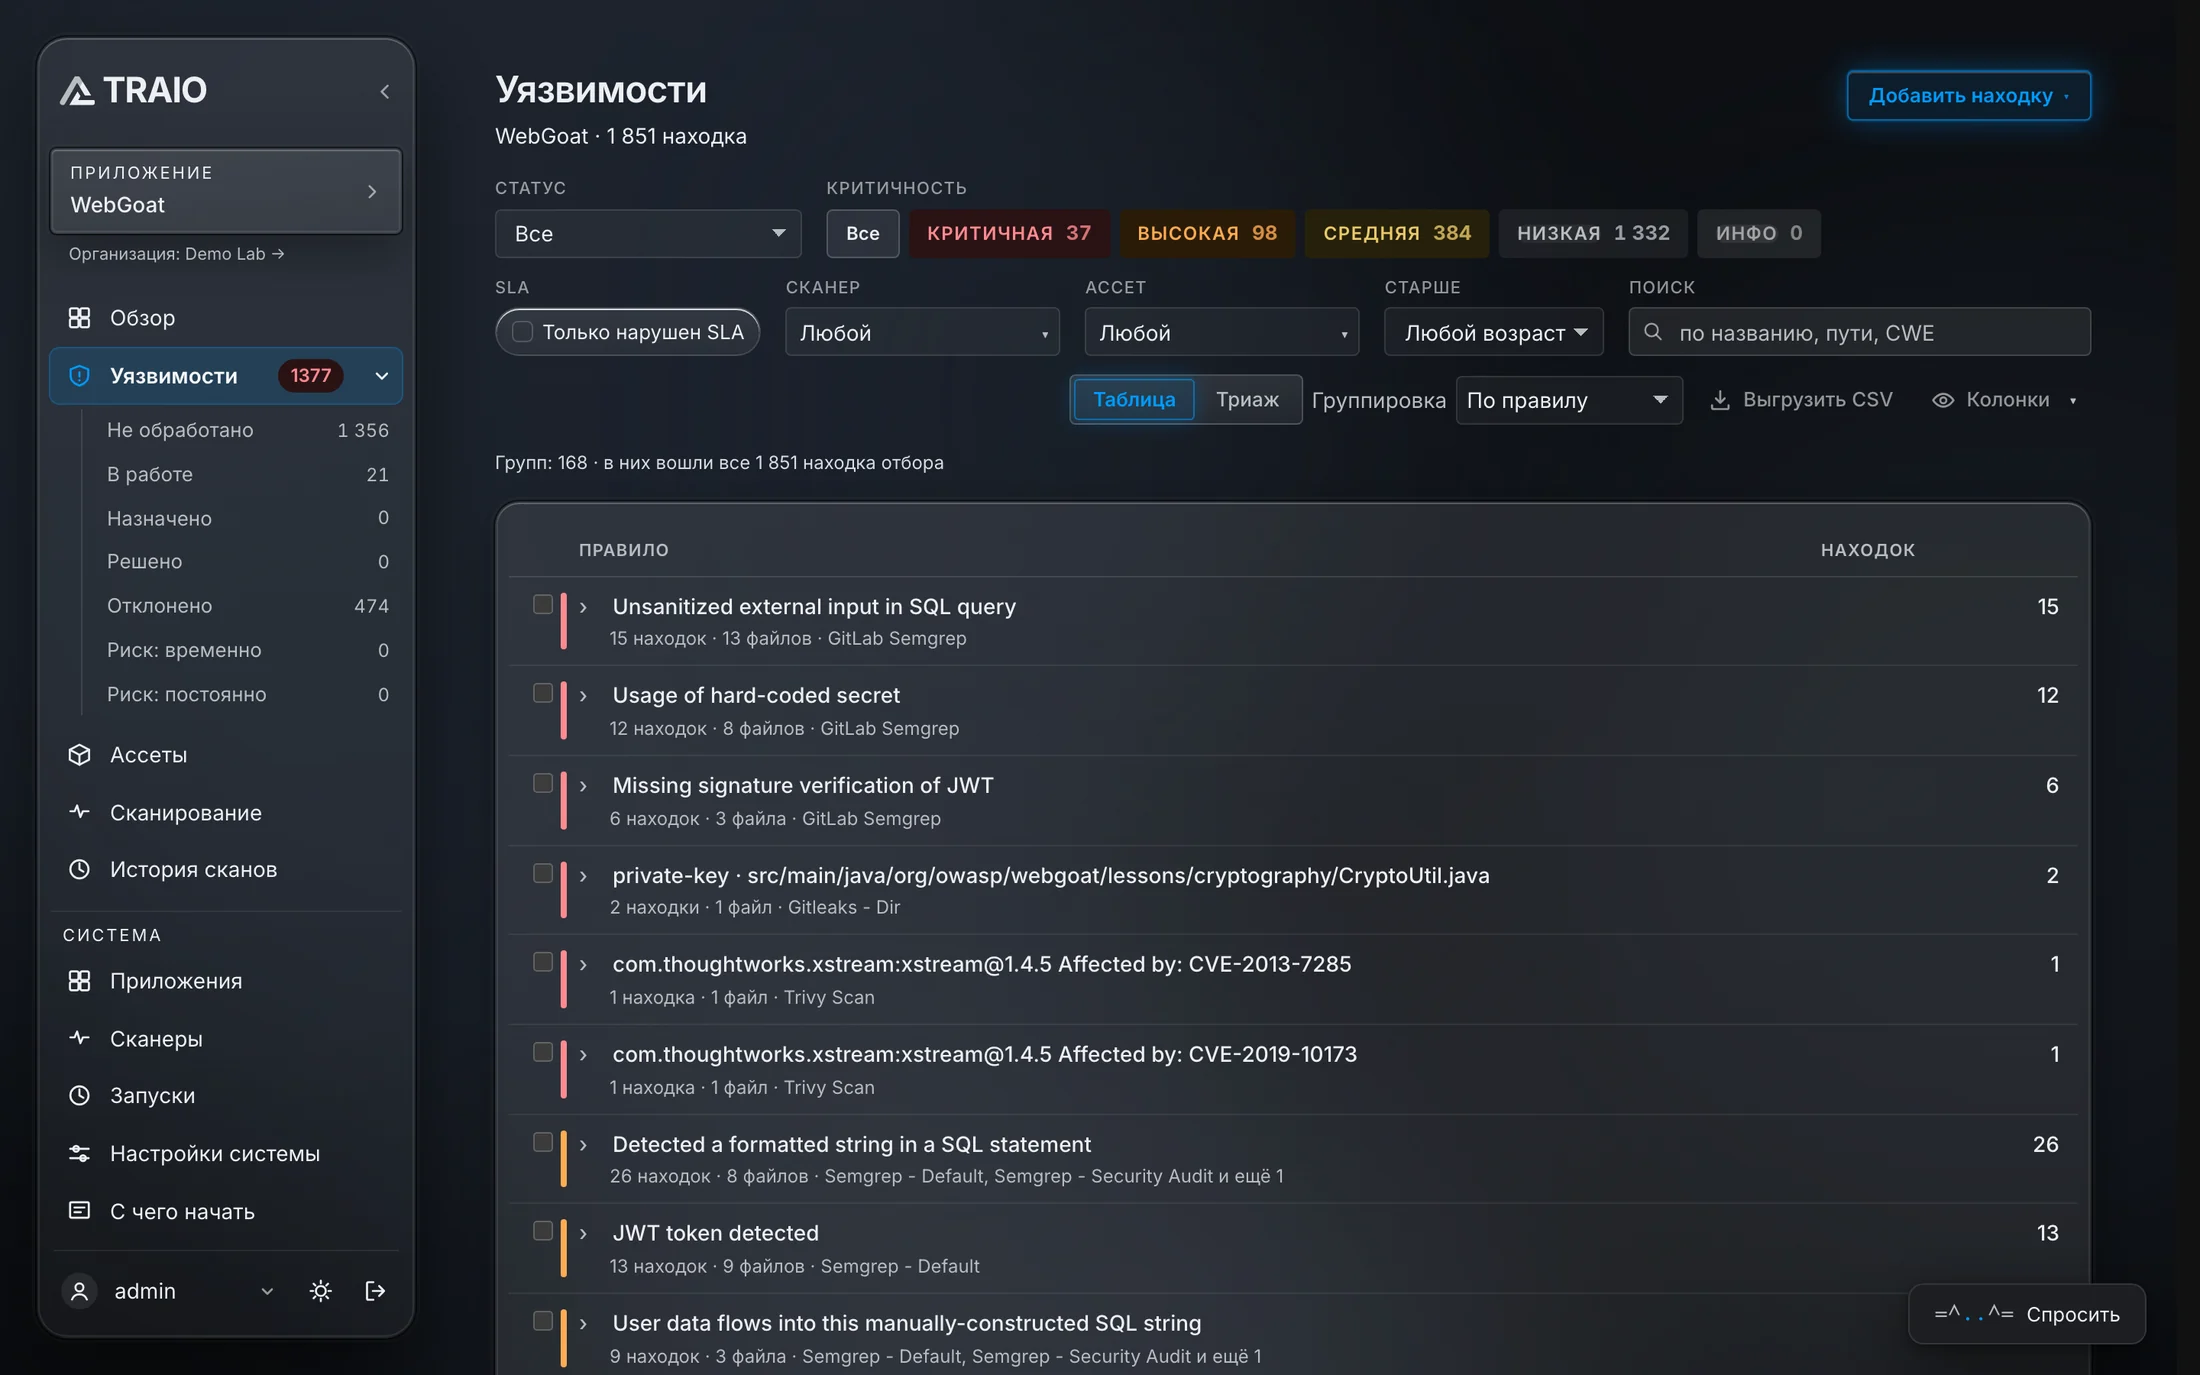
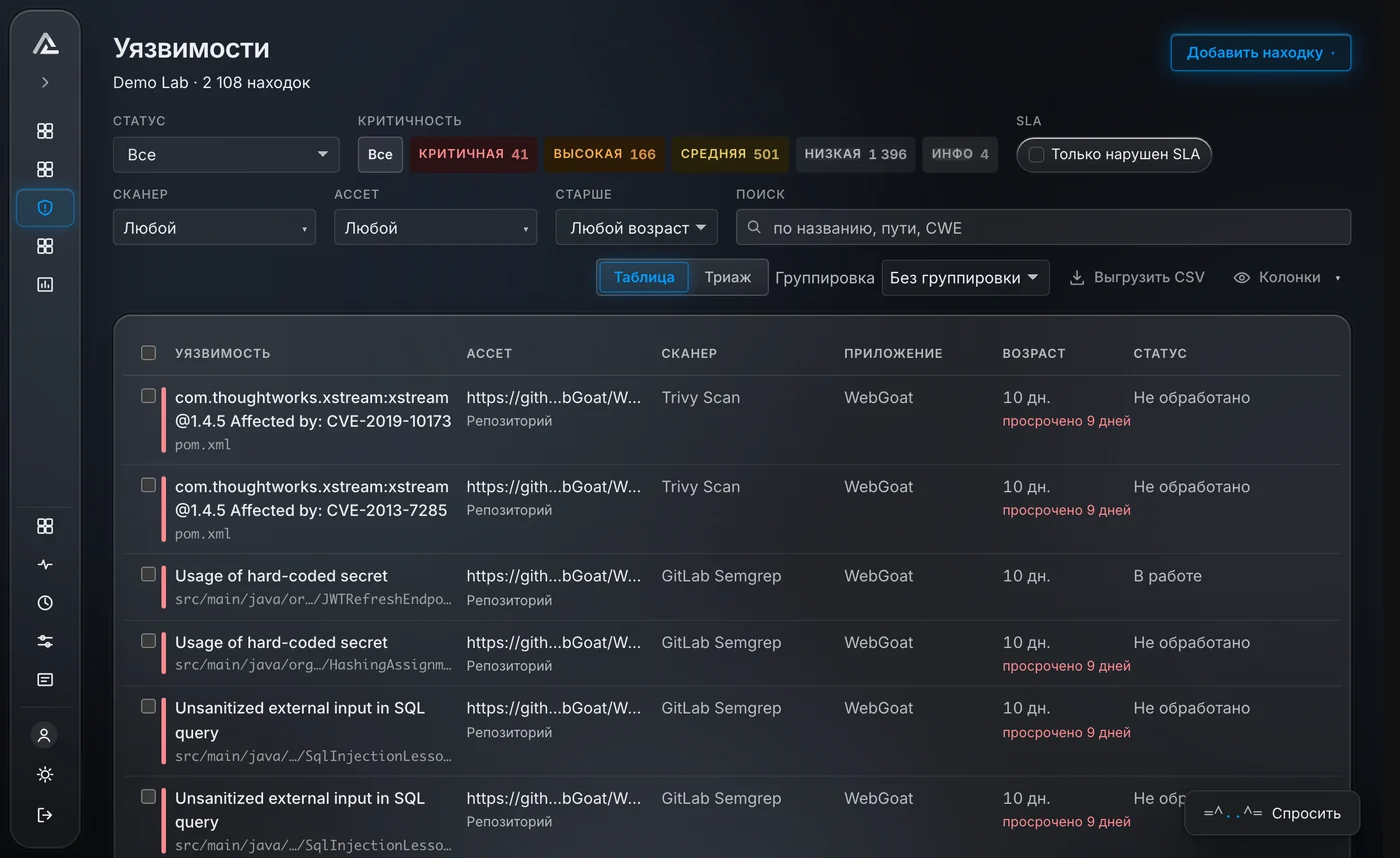
All findings. One list.
Findings from all scanners in one table, with filters by severity, status, deadline, scanner, asset and application.
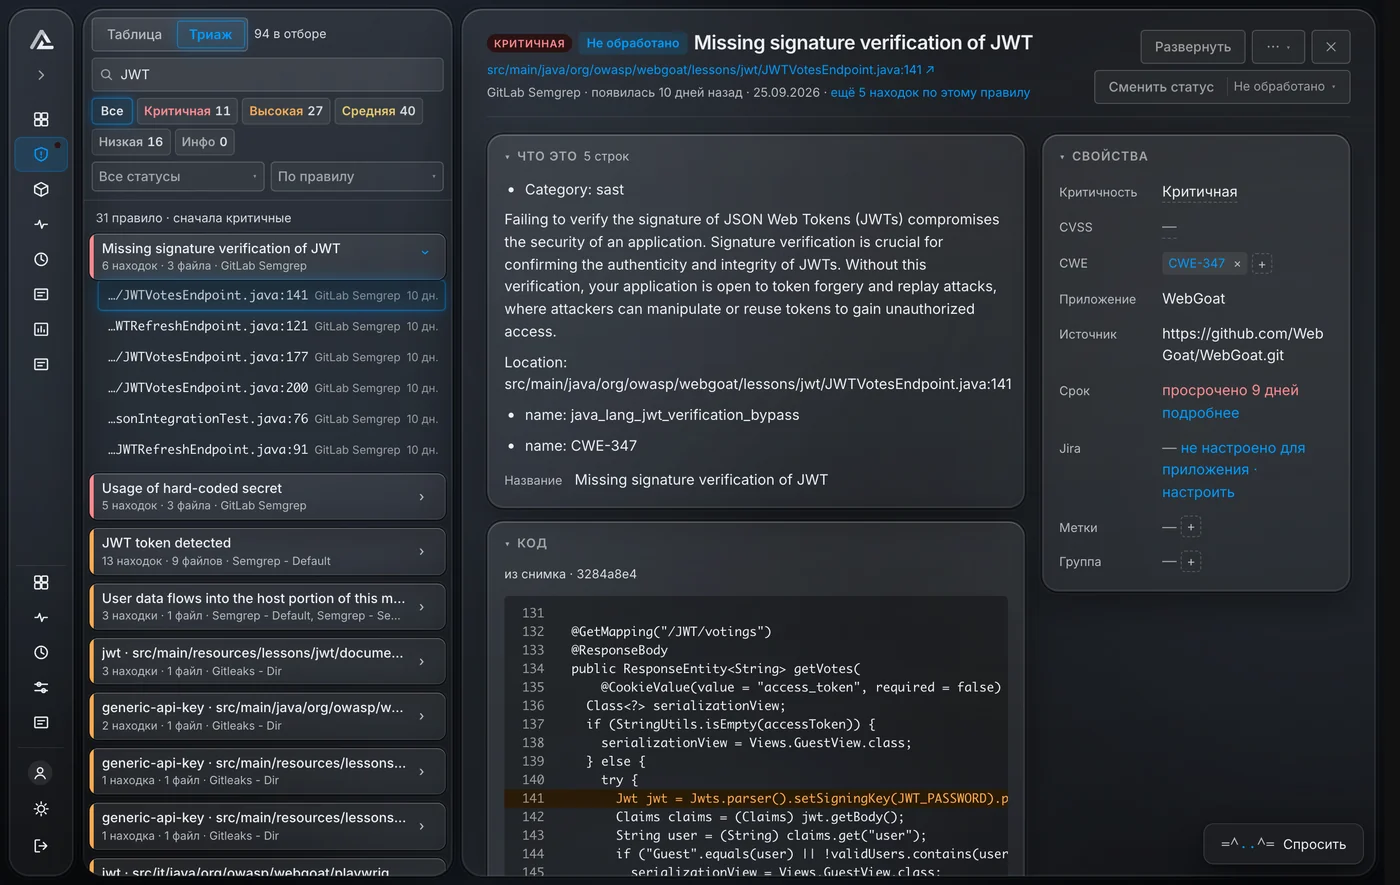
Full context for every vulnerability
Each finding shows severity, CWE, file and line, repository, deadline and the code snippet right in the card.
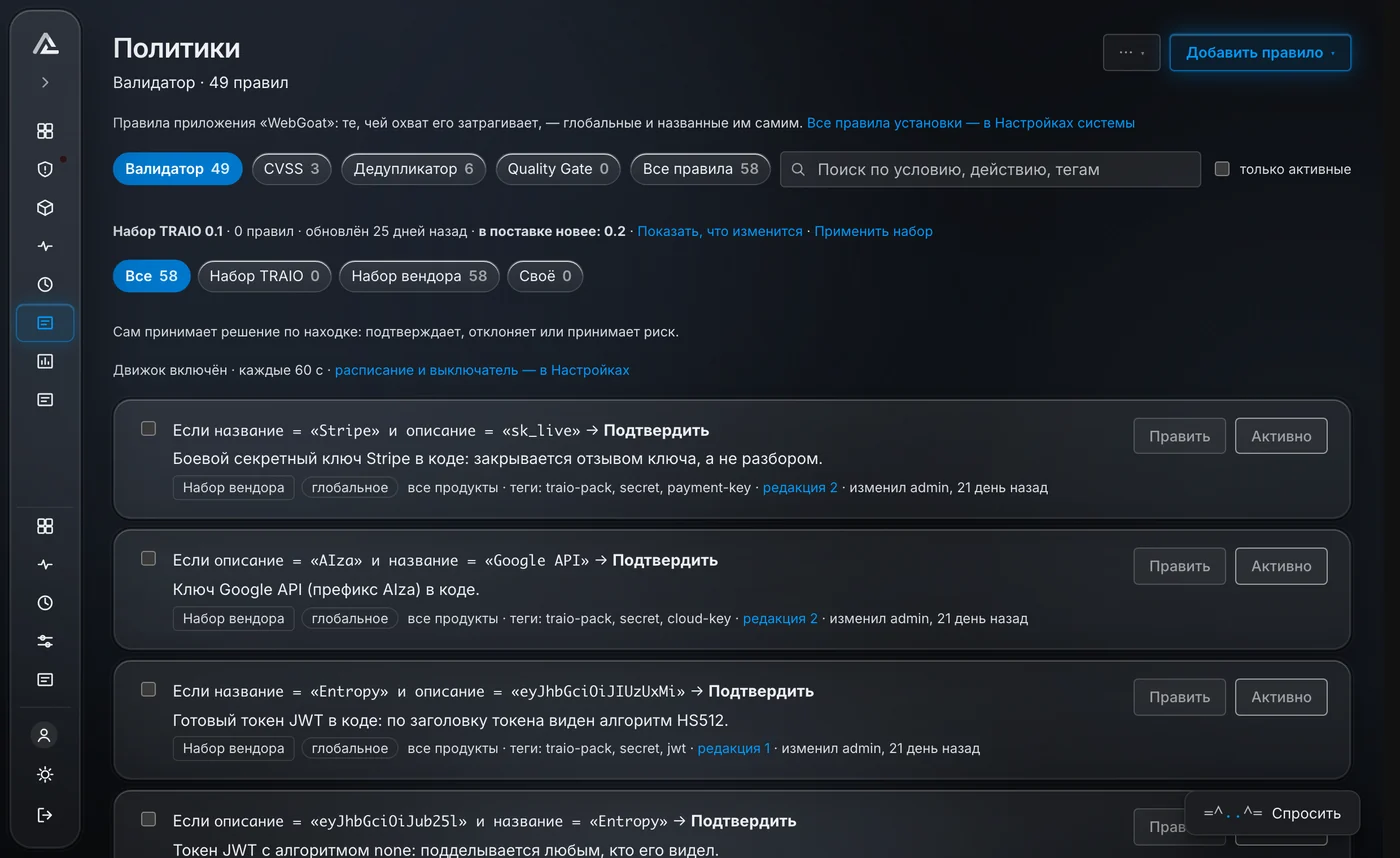
Rules. Less manual work.
The validator makes the decision on a finding itself: it confirms, rejects or accepts the risk, according to your rules.
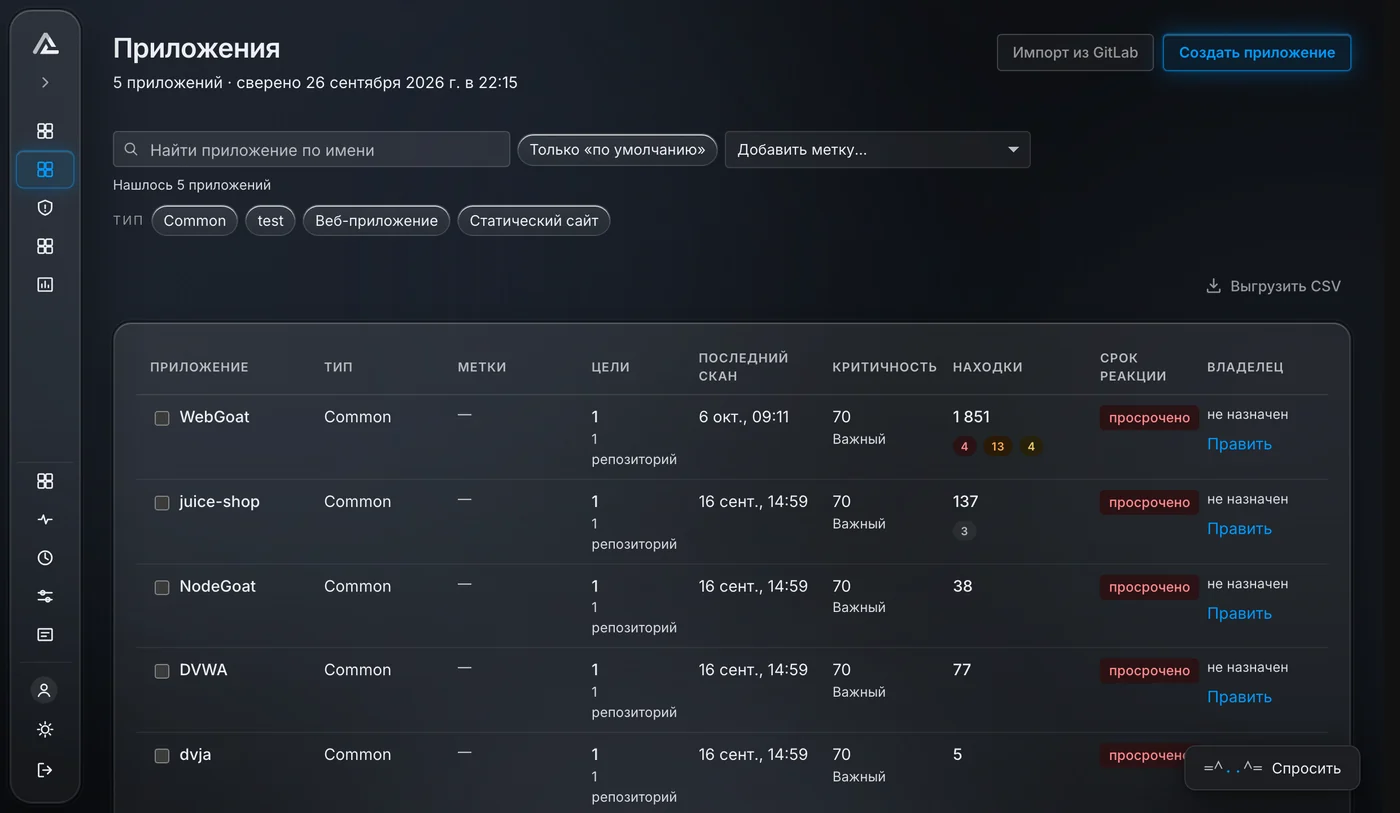
All applications in one place
Repositories, archives, Docker images, domains, hosts and cloud accounts, linked to applications.
Works with your stack
- Automatic repository import
- Scanning by webhook and on every commit
- Comments in Merge Requests
- Blocking MRs by security criteria
- Automatic creation of tasks for vulnerabilities
- Two-way status synchronization
- Webhook support
- Connect an organization with a single token
- Repository import with sorting into applications
- Webhook on push
Kazakhstan regulator and PCI DSS requirements
TRAIO covers secure development requirements from the key documents. It works in networks connected to the national internet gateway (ESHDI), with its trusted certificates preinstalled.
Information security requirements for banks. Replaced NBK Resolution No. 48 starting April 2026.
Unified requirements for the government sector: testing software for information security compliance before commissioning.
Resolution of the National Bank of the Republic of Kazakhstan on information security requirements for financial organizations.
International security standard for payment card data.
Review of information security requirements for Kazakhstan's banks
Two license options
All modules, users and projects without limits. Only asset accounting differs. Both options are On-Premise; a cloud version is not offered.
Licensed by number of assets and scales with the size of your infrastructure.
- Full functionality: SAST, DAST, SCA, Container Security, MAST
- Unlimited users, streams and projects
- Limited by number of assets
- On-Premise
Fixed price on request, with no limit on the number of assets.
- Full functionality: SAST, DAST, SCA, Container Security, MAST
- Unlimited users, streams and projects
- Unlimited number of assets
- On-Premise
System requirements
Ubuntu 22.04 LTS, Docker and Docker Compose. Two virtual machines: TRAIO Platform and TRAIO CI. Any Linux distribution is supported via Docker. Network ports: HTTPS/HTTP (443/80).
- CPU: 4 cores
- RAM: 8 GB
- Storage: 60 GB SSD
- OS: Ubuntu 22.04.5+ LTS
- Docker + Compose
per VM
- CPU: 4 cores
- RAM: 16 GB
- Storage: 100 GB SSD
- OS: Ubuntu 22.04.5+ LTS
- Docker + Compose
per VM
What people say about TRAIO
“Adding your own scanners, customizing any tool, and not touching the pipelines? Yes, that already exists. TRAIO runs scans on triggers by itself and does not break the usual development process.”
“Convenient and intuitive interface, minimal time for the team to learn it. Very fast integration with current development processes, without the need to rebuild CI/CD pipelines.”
“I tested the product on my own test project, and I liked its ease of use and flexibility of configuration.”
Joint development by TRIDS and AST Cyber Lab
TRAIO is developed by the Kazakh company TRIDS (Triangle DevSecOps Services LLP) with the participation of AST Cyber Lab. AST Cyber Lab supplies and implements TRAIO, and helps with the pilot and integration into development processes at banks, government bodies and IT companies in Kazakhstan and Central Asia.
- Demonstration and pilot on your infrastructure
- On-Premise deployment and connection of GitLab, GitHub, Jira
- Setup of rules, Quality Gate and audit reporting
- Training for development and AppSec teams
AST Cyber Lab office in Almaty. We work with companies across Kazakhstan and in Central Asian countries: Uzbekistan, Kyrgyzstan, Tajikistan, Turkmenistan.